posted in Selfhosted

For those selfhosting stuff that's publicy accessible, do you serve a security.txt?
en.wikipedia.org/wiki/Security.txt
Reposted from r/selfhosted.
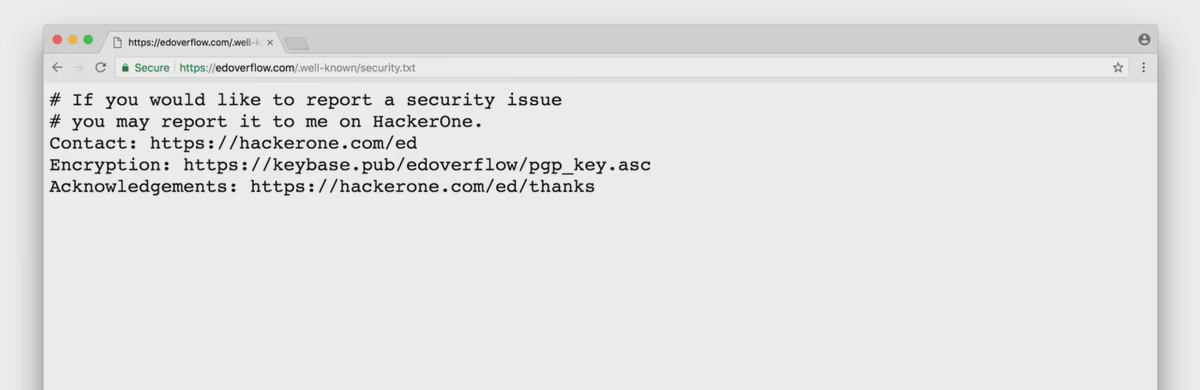 en.wikipedia.orgsecurity.txt - Wikipedia
posted in Selfhosted
For those selfhosting stuff that's publicy accessible, do you serve a security.txt?
en.wikipedia.org/wiki/Security.txt
Reposted from r/selfhosted.
en.wikipedia.orgsecurity.txt - Wikipedia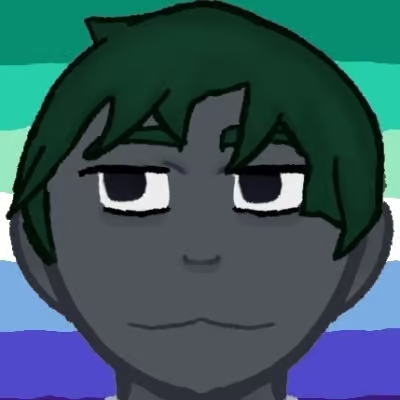
Replying to @nawan@scribe.disroot.org
Yes, but I should probably also put one up on my other domains
Replying to @oha@lemmy.pobierz.net
Nice domain!
Replying to @B0rax@feddit.org
Replying to @B0rax@feddit.org
thanks!

I was gonna say you had it in the wrong place, but it looks like you also serve it in the /.well-known/ location as well.
Replying to @nawan@scribe.disroot.org
Nope, maybe I should ! Thanks for the reminder !
Replying to @nawan@scribe.disroot.org
No, because it invites beg bounties and slop reports.
Replying to @slazer2au@lemmy.world
If you run any sort of public facing website, you’ll likely get some of those eventually.
Replying to @synestine@sh.itjust.works
Inherently this. Keeping security/spam/admin@ open are generally benevolent behaviors for the internet. The more appropriate response is to start blocking domains and hosting providers from contacting those channels. If someone cares, they’ll reach out.
Microsoft properties on the other hand, can suck my whole asshole.
Replying to @nawan@scribe.disroot.org
Why so people ignore that too?
Replying to @nawan@scribe.disroot.org
No, it’s free real estate for scams, slop and the like.
Replying to @nawan@scribe.disroot.org
Do people actually contact you with that?
Replying to @majster@lemmy.zip
I have a security.txt with an email to report vulnerabilities and a public key to encrypt sensitive information. The only reports I ever got were on the contract us form, unencrypted.
Yep. Looots of phishing emails.
Replying to @nawan@scribe.disroot.org
I do, but with a few tweaks that cut most of the junk the other comments mention:
Contact: at a dedicated alias, not your main inbox, and filter it hard. If the noise gets bad you can drop the alias without touching anything else.Policy: line linking to a short page that says plainly there is no bug bounty and no payment for reports. Most beg-bounty mails are mass-sent with a payment ask, so this gives you something to point them at and lets you bin them without guilt.Expires:, it’s actually required by RFC 9116 and a lot of hand-written files leave it out. Set a calendar reminder to bump it./.well-known/security.txt; the root path is only a legacy fallback.Whether it’s worth it for a homelab is debatable, but if you host anything other people rely on (a Matrix/Lemmy instance, a shared Nextcloud), having one real contact path beats someone finding a hole and having nowhere to send it.