posted in Selfhosted

For those selfhosting stuff that's publicy accessible, do you serve a security.txt?
en.wikipedia.org/wiki/Security.txt
Reposted from r/selfhosted.
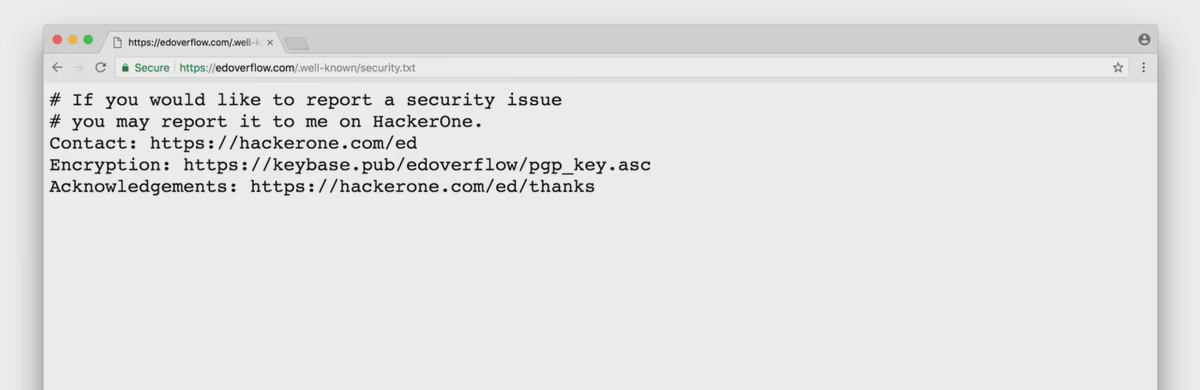 en.wikipedia.orgsecurity.txt - Wikipedia
posted in Selfhosted
For those selfhosting stuff that's publicy accessible, do you serve a security.txt?
en.wikipedia.org/wiki/Security.txt
Reposted from r/selfhosted.
en.wikipedia.orgsecurity.txt - WikipediaReplying to @nawan@scribe.disroot.org
No, because it invites beg bounties and slop reports.
Replying to @slazer2au@lemmy.world
If you run any sort of public facing website, you’ll likely get some of those eventually.
Replying to @synestine@sh.itjust.works
Inherently this. Keeping security/spam/admin@ open are generally benevolent behaviors for the internet. The more appropriate response is to start blocking domains and hosting providers from contacting those channels. If someone cares, they’ll reach out.
Microsoft properties on the other hand, can suck my whole asshole.