Replying to @⁨Edent@mastodon.social⁩

Well this is exciting!

My little #ActivityBot server is through to the next round of the @nlnet grant application process.

Still a long way to go, but rather encouraging.

You can play with the code at gitlab.com/edent/activity-bot/

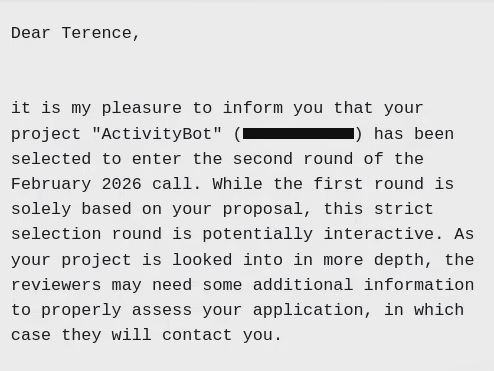
Screenshot of an email. Dear Terence, it is my pleasure to inform you that your project "ActivityBot" has been selected to enter the second round of the February 2026 call. While the first round is solely based on your proposal, this strict selection round is potentially interactive. As your project is looked into in more depth, the reviewers may need some additional information to properly assess your application, in which case they will contact you. — Open image attachment ⁨1⁩ of ⁨1⁩
Screenshot of an email. Dear Terence, it is my pleasure to inform you that your project "ActivityBot" has been selected to enter the second round of the February 2026 call. While the first round is solely based on your proposal, this strict selection round is potentially interactive. As your project is looked into in more depth, the reviewers may need some additional information to properly assess your application, in which case they will contact you.
en

Replying to @⁨Edent@mastodon.social⁩

I'm going to try and keep a record of all the bugs, errors, and inconsistencies I've reported in #ActivityPub and #Mastodon documentation.

First up, how big are the limits on what you can federate?

Mastodon lists some limits in KB/MB, but others are just raw numbers. That might make sense for an ASCII world - but emoji complicate everything.

github.com/mastodon/mastodon/i

github.com/mastodon/mastodon/issues/40290

Replying to @⁨Edent@mastodon.social⁩

A weird #ActivityPub message from #Frendica.

Signed on 2026-09-01
Published on 2026-03-02

That's a skew of six months! The message type is "Undo" - so they're undoing a like they sent in March.

Is there *really* a worry about accepting requests like this? Given the message has been signed, what risk is there to replay attacks?

Bug report at github.com/friendica/friendica

github.com/friendica/friendica/issues/16150
I have searched open and closed issues for duplicates Bug Description My AP server has received an Undo request from a server running Friendica 'Blutwurz' 2026.05-1595 The header which contains the...GitHubUndo published timestamp doesn't match signature date · Issue #16150 · friendica/friendicaI have searched open and closed issues for duplicates Bug Description My AP server has received an Undo request from a server running Friendica 'Blutwurz' 2026.05-1595 The header which contains the...by edent

Replying to @⁨Profpatsch@mastodon.xyz⁩

@Profpatsch @Edent

An HTTP signature proves that an activity exists on the originating server - it's substitute for fetching activity by its ID. The originating server has full control over the activity JSON and the request headers, so the date of publishing doesn't matter.

What may matter is the date when the signature itself was created. If you receive a request signed several days ago, that might indicate a replay attack... Or a broken clock on the sender side.