Can someone confirm for me using a non robot answer that to have package attestations on pypi, your entire build process and upload must entirely take place using a commercial CI provider such as GitHub actions. It will never be possible to do the actual build on your local machine anymore and twine is effectively a thing of the past if you want your packages to be trusted. This is what I'm being told
Replying to @⁨zzzeek@hachyderm.io⁩

right as I'm preparing to work up a comprehensive migration of my whole release architecture across six projects to use github actions, because I care about supply chain attacks and pep-740 compliance currently requires one of a very small list of trusted hosts

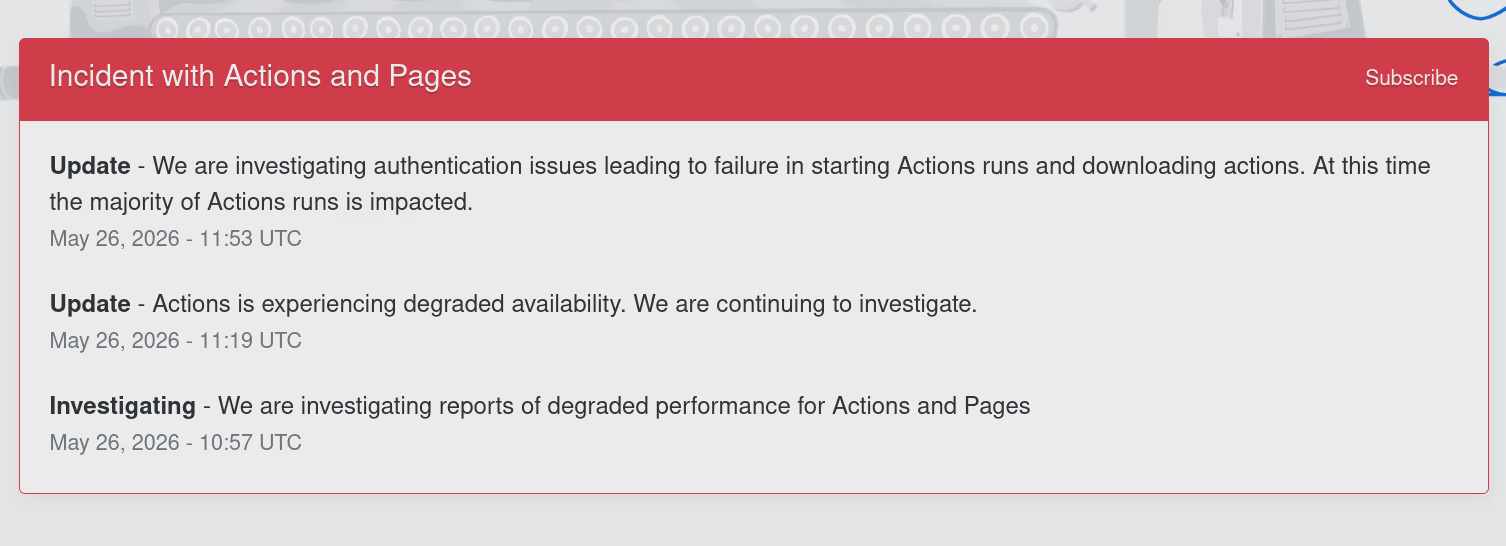
screenshot from github

Incident with Actions and Pages
Subscribe
Update - We are investigating authentication issues leading to failure in starting Actions runs and downloading actions. At this time the majority of Actions runs is impacted.
May 26, 2026 - 11:53 UTC
Update - Actions is experiencing degraded availability. We are continuing to investigate.
May 26, 2026 - 11:19 UTC
Investigating - We are investigating reports of degraded performance for Actions and Pages
May 26, 2026 - 10:57 UTC
— Open image attachment ⁨1⁩ of ⁨1⁩
screenshot from github Incident with Actions and Pages Subscribe Update - We are investigating authentication issues leading to failure in starting Actions runs and downloading actions. At this time the majority of Actions runs is impacted. May 26, 2026 - 11:53 UTC Update - Actions is experiencing degraded availability. We are continuing to investigate. May 26, 2026 - 11:19 UTC Investigating - We are investigating reports of degraded performance for Actions and Pages May 26, 2026 - 10:57 UTC
en